Tech
Why Indian IT Firms Are Investing in SAFe Scrum Master Certification

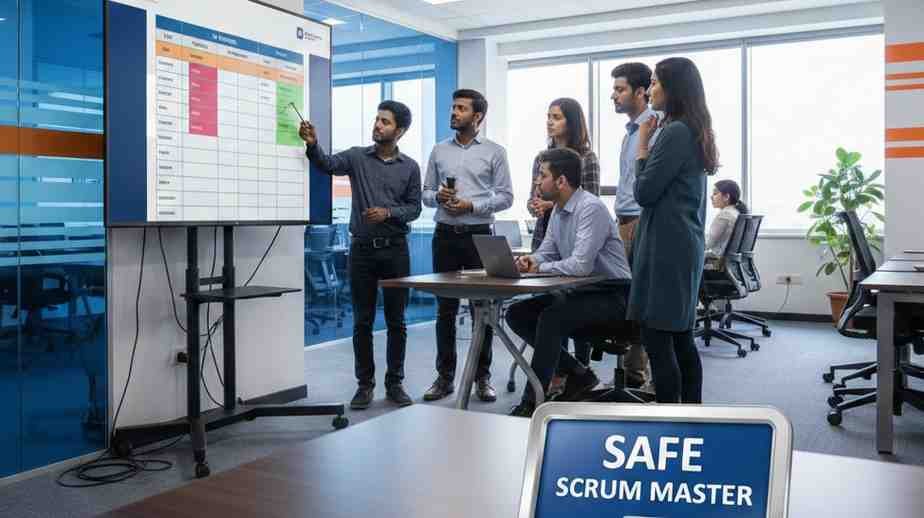
India’s IT sector is on an extraordinary growth trajectory. According to NASSCOM, the industry is expected to cross $300 billion in revenue by 2026, driven by digital transformation, AI adoption, and the rapid expansion of Global Capability Centres (GCCs). But behind these impressive numbers lies a growing challenge — the demand for skilled agile professionals is far outpacing supply. This is precisely why Indian IT firms, from Bengaluru’s tech corridors to Mumbai’s financial district, are investing heavily in SAFe certification.
The Agile Imperative in Indian IT
India’s IT industry no longer operates on traditional waterfall models. Clients across the globe now expect faster delivery cycles, continuous integration, and the ability to pivot quickly. Agile is no longer a competitive advantage — it is the baseline expectation.
However, scaling agile across large organisations with thousands of developers, multiple product lines, and distributed teams is a fundamentally different challenge from running Scrum in a single team. This is where the Scaled Agile Framework (SAFe) has become the framework of choice for India’s leading IT services and product companies. SAFe provides the structure, alignment, and governance needed to implement agile practices at enterprise scale without losing speed or quality.
Why SAFe Scrum Master Certification Is in Demand
At the heart of any successful agile transformation is the Scrum Master — the person responsible for facilitating team ceremonies, removing impediments, and coaching teams on agile principles. But in a scaled environment, the role demands far more. A SAFe Scrum Master must understand how their team fits into a larger Agile Release Train (ART), how to coordinate across multiple teams, and drive relentless improvement at both the team and programme levels.
This is why SAFe Scrum Master Certification has become one of the most sought-after credentials in the Indian IT market. It validates a professional’s ability to operate effectively within the SAFe framework, lead agile teams at scale, and support PI (Programme Increment) planning — all critical capabilities for organisations serving global enterprise clients.
Mumbai’s Growing Role in India’s Agile Story
While Bengaluru has long been considered India’s tech capital, Mumbai is rapidly emerging as a major hub for IT services, fintech, and digital transformation. The city is home to some of India’s largest financial institutions, consulting firms, and a growing number of GCCs. Companies like TCS, Reliance, and Shapoorji Pallonji Group are driving digital initiatives from Mumbai, and all of them require agile talent at scale.
For professionals based in or around Mumbai, pursuing SAFe Scrum Master Certification Training in Mumbai offers a direct pathway to tap into this demand. The training equips participants with practical knowledge of SAFe principles, Scrum at scale, Kanban, built-in quality practices, and the tools needed to facilitate effective agile delivery in complex enterprise environments.
The GCC Factor
One of the biggest drivers of SAFe adoption in India is the explosive growth of Global Capability Centres. India now hosts over 1,700 GCCs, and this number is climbing rapidly. These centres are no longer back-office operations — they function as strategic innovation hubs for global corporations. GCCs demand structured agile practices that align with their parent organisations’ delivery frameworks, and SAFe is overwhelmingly the preferred choice.
For Scrum Masters working in or aspiring to join GCCs, holding a SAFe Scrum Master Certification is increasingly becoming a non-negotiable requirement. It demonstrates that you can operate within a globally recognised framework and contribute to enterprise-level agile delivery from day one.
The Career and Salary Advantage
The financial case is equally compelling. India’s IT hiring is rebounding strongly, with over 150,000 fresher hires expected in FY25 alone. Professionals with SAFe credentials consistently command higher salaries and faster career progression than their non-certified peers. Roles such as SAFe Scrum Master, Release Train Engineer, and Agile Coach are among the most in-demand positions across India’s top IT employers.
Enrolling in SAFe Scrum Master Certification Training in Mumbai is not just a training investment — it is a career accelerator in one of the world’s fastest-growing tech markets.
Final Thought
India’s IT industry is scaling at a pace that demands structured, certified agile leadership. The firms that invest in SAFe capability today will be the ones delivering the most value tomorrow. Whether you are an aspiring Scrum Master or a seasoned IT professional, now is the time to get certified and lead the agile transformation that Indian IT is counting on.

Modern applications operate in increasingly complex digital environments where cyber threats continue evolving in sophistication and frequency. Mobile apps, APIs, cloud-native platforms, and enterprise software face constant risks from reverse engineering, code tampering, credential theft, and runtime attacks. While traditional application protection remains an important layer of defence, organisations are increasingly seeking more adaptive security approaches that can respond to threats as they occur rather than relying solely on preventive measures. Many security teams now evaluate alternative to Guardsquare that provide broader runtime visibility, continuous monitoring, and stronger protection against emerging attack techniques.
As application security strategies continue advancing, organisations are placing greater emphasis on technologies that combine code protection with intelligent threat detection, automated response, and real-time risk analysis. These capabilities help security teams strengthen application resilience while supporting secure digital transformation across modern business environments.
Modern Application Protection Supporting Continuous Cyber Resilience
Modern application security combines preventive controls with real-time visibility, intelligent monitoring, and adaptive protection to reduce cyber risks while supporting resilient software environments.
1. Adaptive Threat Detection Strengthens Protection
Modern security platforms increasingly rely on behavioural analytics, artificial intelligence, and machine learning to identify unusual application behaviour. Rather than relying solely on predefined signatures, adaptive detection analyses runtime activity to recognise emerging attack patterns. This proactive approach enables organisations to detect previously unknown threats while reducing false positives and improving overall security effectiveness across complex application environments.
2. Integrated Security Simplifies Operations
Application security becomes more effective when multiple protective capabilities operate through a unified platform. Integration between runtime monitoring, vulnerability management, threat intelligence, and incident response enables security teams to investigate threats more efficiently while reducing operational complexity. Centralised visibility also improves collaboration between development, operations, and security teams throughout the software lifecycle.
3. Runtime Monitoring Improves Threat Visibility
Traditional application protection focuses primarily on safeguarding applications before deployment. As cyber threats continue to become more dynamic, organisations increasingly evaluate solutions that extend protection beyond static code security. An alternative to Guardsquare may offer runtime monitoring capabilities that detect suspicious behaviour, identify malicious activity, and provide security teams with actionable intelligence while applications remain operational. Continuous monitoring improves visibility into evolving threats and enables organisations to respond more effectively before security incidents escalate.
4. Automation Accelerates Incident Response
Automation helps organisations respond quickly to security events. Intelligent security platforms can automatically identify suspicious activity, trigger alerts, initiate predefined response actions, and collect forensic information for further investigation. Faster response times reduce potential business disruption while helping organisations minimise the impact of cyber incidents before they spread across critical systems.
5. Cloud-Native Protection Supports Digital Transformation
As organisations increasingly migrate workloads to cloud environments, security solutions must adapt to distributed infrastructures. Modern application protection platforms provide scalable security that supports cloud-native applications, microservices, APIs, and containerised environments. Flexible deployment models enable businesses to maintain consistent protection while supporting continuous software delivery and rapidly evolving development practices.
Building Resilient Security for Modern Applications
Application security continues evolving beyond traditional preventive controls as organisations seek greater visibility, faster threat detection, and stronger protection against increasingly sophisticated cyber threats. Modern security strategies combine runtime monitoring, intelligent analytics, behavioural detection, automation, and continuous security validation to protect applications throughout their operational lifecycle. By adopting a proactive approach, organisations can identify emerging risks earlier, respond more efficiently to security incidents, and reduce potential operational disruptions.
Continuous monitoring also strengthens compliance, improves collaboration between development and security teams, and supports secure software delivery across cloud-native and hybrid environments. As digital transformation accelerates, resilient application security frameworks help businesses safeguard critical assets, maintain customer trust, support regulatory requirements, and confidently drive long-term innovation in an increasingly connected digital landscape.
Advancing Application Security Through Intelligent Defence
Modern application security strategies focus on continuous visibility, proactive threat detection, and intelligent response mechanisms that help organisations strengthen resilience against evolving cyber risks while supporting secure software innovation.
1. Strengthening API and Mobile Application Security
Applications increasingly rely on APIs and mobile platforms to deliver digital services, making them attractive targets for cybercriminals. Protecting these environments requires multiple layers of security that safeguard sensitive data, prevent unauthorised access, and detect abnormal behaviour during runtime. Continuous protection helps organisations reduce exposure to attacks while maintaining secure digital experiences for users across various devices and operating systems.
2. Improving Security Across Development Lifecycles
Embedding security throughout the software development lifecycle enables organisations to identify vulnerabilities earlier while reducing remediation costs. Security testing, code analysis, runtime monitoring, and continuous validation support stronger software quality without slowing development. Integrating security into DevSecOps workflows also encourages closer collaboration between development and security teams while improving application resilience before and after deployment.
3. Supporting Compliance and Risk Management
Many organisations operate within industries that require strict compliance with regulatory and security standards. Effective application security solutions help maintain audit readiness through detailed monitoring, reporting, and visibility into security events. Improved governance enables organisations to demonstrate stronger control over application environments while supporting evolving regulatory requirements and internal risk management objectives.
4. Enabling Continuous Security Improvement
Cybersecurity requires ongoing evaluation rather than one-time implementation. Continuous assessment of application behaviour, threat intelligence, and emerging attack techniques enables organisations to strengthen security strategies over time. Regular monitoring and adaptive protection help businesses respond more effectively to new vulnerabilities while maintaining resilient application environments that support long-term operational stability.
5. Building Future-Ready Cybersecurity Strategies
As digital ecosystems continue to expand, organisations require security solutions capable of adapting to technological change. Combining intelligent monitoring, automated response, behavioural analytics, and runtime protection enables businesses to build more resilient cybersecurity frameworks. A proactive approach supports secure innovation while helping organisations confidently manage evolving application security challenges across modern digital environments.
Conclusion
As cyber threats continue to become more sophisticated, organisations increasingly seek security platforms that combine application protection with intelligent runtime monitoring, adaptive threat detection, and automated response capabilities. Modern security solutions help businesses strengthen application resilience, improve operational visibility, and respond more effectively to emerging cyber risks across increasingly complex digital environments.
Businesses evaluating modern application security platforms may consider Doverunner as part of their broader security strategy. Doverunner provides runtime application protection, real-time threat detection, behavioural monitoring, and intelligent security capabilities designed to help organisations strengthen application security throughout the software lifecycle. By combining advanced protection with continuous visibility and proactive defence, they help organisations build more resilient, secure, and future-ready application environments.
Launching a new DTC brand on Shopify in 2026 is both easier and harder than it used to be. Easier because the platform itself has matured, Shopify now handles international markets, subscriptions, B2B, and headless natively without heroic workarounds. Harder because the standard for “good” has risen. Customers expect sub-second page loads, personalized product discovery, and checkout flows as slick as Amazon’s. The DIY theme-store approach that worked in 2018 rarely clears the bar in 2026.
Which is why most DTC brands launching seriously, not testing the water, but committing to building a business, work with a Shopify agency from day one. Here’s a shortlist of agencies that show up repeatedly in DTC founder conversations, grouped by what they specialize in.
Technical-first agencies (engineering-heavy builds)
If your brand has non-trivial technical requirements, complex bundles, subscription intervals, international currency needs, custom integrations, these agencies are the ones DTC founders hire.
Netalico, Los Angeles, CA
Boutique Shopify Plus agency focused on custom development and performance optimization. Good fit for launches where the build has significant custom engineering (ERP integrations, subscription logic, custom theme builds) rather than “pick a theme and tweak it.” 15-30 person team. Shopify Plus Partner. Mid-market pricing. For brands exploring top Shopify agencies with real engineering depth, Netalico is a common shortlist entry. They also offer productized services (CRO audit, ADA compliance audit) that are useful even if you’re not hiring them for the full build.
Fuel Made, Seattle, WA
Mid-market US-based Plus partner. Strong post-launch retainer practice. Often the right choice for DTC brands that want the same team to launch the store and grow it.
Swanky, Brighton, UK
Plus Elite partner with strong CRO retainer practice. If your launch is in the UK/EU market, Swanky has market-specific knowledge worth paying for.
Full-service launch partners (brand + build + growth)
These agencies can take you from an idea with a brand brief to a shipping store with first-month paid media running.
Barrel, New York, NY
Brand agency with an ecommerce practice. Best fit if your launch is heavy on positioning and brand identity. Notable DTC clients include Sakara and SpaceNK. Enterprise pricing.
Tinuiti
Omnichannel agency with Shopify practice. Best fit if paid media is the primary growth lever and the store is downstream of that. Often the right call for venture-backed DTC launches with heavy ad budgets.
Bear Group, Seattle, WA
Mid-market engineering-focused shop. Works across apparel, CPG, and home goods. Long-standing Shopify Plus Partner with a strong technical reputation.
Design-forward agencies (aesthetic-first launches)
For fashion, beauty, and lifestyle brands where design quality is the entire value proposition.
Underwaterpistol, Glasgow, UK
Design-led Plus builds for brands like Tangle Teezer and Pip & Nut. Shopify Plus Elite.
Fostr, Denver, CO
Younger agency, strong design portfolio in DTC apparel and beauty. Shopify Plus Partner.
We Make Websites, London, UK
Premium brand-led Shopify Plus builds. Enterprise pricing. If your launch is in the beauty or luxury space, they’re the UK reference agency.
How to decide: a framework for a DTC launch
1. Know your launch budget range
Ballpark realistic ranges for a serious DTC launch on Shopify in 2026:
- $15-40k, Theme-based store with light customization. One designer/developer for 4-6 weeks. Limited integrations. Good enough for testing product-market fit, not for scaling to $1M.
- $40-100k, Custom theme built on a good base (Dawn, Impulse, or similar). Light custom development. 2-3 integrations (email, reviews, analytics). Ships in 8-12 weeks. Fits most launches that have a committed budget and modest timeline.
- $100-250k, Plus tier. Custom build from the ground up. Complex integrations. Full design sprint. 12-20 week timeline. Appropriate for well-funded DTC launches or migrations of existing brands to Plus.
- $250k+, Enterprise Plus. Usually for brands with existing revenue migrating into a more complex technical environment (headless, multi-region, B2B/DTC split).
Match the agency to the budget. Enterprise agencies don’t take $50k projects. Boutiques can be stretched thin on $500k builds. Picking mismatched is the #1 cause of launch pain.
2. Decide: hire an agency or hire a Shopify developer directly?
Some launches are actually better served by a senior freelance Shopify developer than by an agency. Signs you want a developer, not an agency:
- Budget is under $30k
- You have in-house project management
- Scope is clear and narrow
- You need speed more than polish
Signs you want an agency:
- Budget is $40k+
- You don’t have in-house technical leadership
- Scope is uncertain or likely to evolve
- You need brand strategy, design, and engineering from the same vendor
- Post-launch support matters as much as the launch itself
3. Shortlist three across size tiers
Boutique, mid-size, enterprise. Get proposals from each. The pricing spread will be 3-5x wide. That spread is your signal, it tells you what the work is actually worth at each service level.
4. Run a paid discovery before full commitment
Every agency should offer a discovery phase. Pay for it. The output of the discovery phase (technical scope, architecture, risk register, revised estimate) is a working sample of what the full engagement will feel like. If the discovery output is weak, the build will be weak.
Common launch mistakes
Picking the cheapest bid. Shopify builds are not commodity work. The cheapest bid almost always signals junior team composition or unrealistic timeline assumptions.
Overscoping the MVP. Launches that try to ship “everything perfectly the first time” take 3x as long and rarely pay off. Ship the 60% version. Iterate post-launch with a retainer.
Ignoring post-launch. The agency that builds your store may not be the one that should maintain it. Decide upfront, single vendor through year two, or rotate after launch.
Launching without analytics infrastructure. The first month of post-launch data is irreplaceable. If your GA4, server-side tagging, and attribution stack aren’t clean at launch, you’re flying blind during the most informative period.
Final thought
There is no universally-best Shopify agency for DTC launches. The best agency for your brand is the one that matches your launch’s specific shape, budget, complexity, timeline, and post-launch strategy. The founders who hire well are the ones who spend 4-6 weeks on the decision instead of 4-6 days.
The demand for DevOps Engineer Jobs is booming as businesses embrace automation, scalability, and faster delivery. Companies now seek professionals who can bridge development and operations seamlessly. However, the hiring landscape has evolved. Employers want more than just technical skills — they look for problem-solvers who can handle cloud environments, CI/CD pipelines, and complex deployments. Furthermore, with remote work and offshore software teams becoming common, flexibility and collaboration have become must-haves. This blog explores what today’s employers truly expect from DevOps engineers and how aspiring professionals can stand out in a competitive job market.
1. Mastering Core Technical Skills
Modern employers prioritize engineers who understand the full DevOps lifecycle. Candidates must configure servers, automate builds, and manage deployments. Familiarity with tools like Docker, Jenkins, Kubernetes, and Terraform is now standard. Additionally, cloud expertise in AWS, Azure, or Google Cloud significantly boosts credibility.
However, what sets great engineers apart is the ability to integrate these tools into reliable workflows. Employers value those who can design scalable systems, maintain uptime, and optimize performance. Furthermore, scripting knowledge — especially in Python, Bash, or Go — helps automate repetitive tasks. Understanding monitoring tools like Prometheus or Grafana also demonstrates operational maturity.
In short, recruiters look for engineers who don’t just “use tools” but “build systems.” Those who can connect multiple moving parts into a seamless pipeline are the ones who land top DevOps Engineer Jobs.
2. Strong Understanding of CI/CD and Automation
Automation remains at the heart of every successful DevOps strategy. Employers prefer engineers who can build, manage, and optimize CI/CD pipelines. These pipelines ensure that code moves from development to production quickly and safely. Tools like GitHub Actions, GitLab CI, and CircleCI dominate this space.
Furthermore, companies expect engineers to identify bottlenecks and create automated solutions that reduce manual intervention. They seek professionals who can integrate testing, security, and compliance into these pipelines. This shows foresight and accountability.
Additionally, with distributed and offshore software teams, engineers must ensure smooth collaboration and deployment synchronization. Employers admire candidates who design pipelines resilient to failures and adaptable to multi-cloud environments. In essence, they want automation specialists who deliver reliability, not just speed. Mastering CI/CD isn’t optional anymore — it’s the foundation for every DevOps Engineer Job today.
3. Cloud-Native and Security Mindset
Employers are shifting toward cloud-first and security-driven approaches. Hence, DevOps engineers must deeply understand cloud architecture, networking, and scalability. Knowledge of Kubernetes clusters, load balancers, and IaC tools is essential.
Furthermore, organizations expect engineers to implement security from day one — not as an afterthought. DevSecOps is gaining momentum, and professionals who embed vulnerability scanning and compliance checks directly into pipelines stand out.
Additionally, familiarity with container orchestration, secret management, and zero-trust principles demonstrates maturity in handling enterprise-grade systems. Employers value engineers who treat security as part of development, not a blocker.
The most desirable candidates proactively identify threats, manage access policies, and ensure resilience under pressure. In short, the modern DevOps Engineer Job market rewards those who think like architects and act like guardians — balancing speed with safety across every layer of the stack.
4. Collaboration and Communication
Technical skills alone no longer guarantee success. Employers want DevOps engineers who communicate effectively across teams. After all, DevOps thrives on collaboration between developers, testers, and operations.
Furthermore, companies emphasize cross-functional teamwork. Engineers must explain technical issues to non-technical stakeholders and help teams align around shared goals. Soft skills like empathy, adaptability, and transparency build trust and reduce friction in complex projects.
Additionally, as many organizations work with offshore software teams, collaboration across time zones and cultures has become critical. Engineers who can document clearly, use tools like Slack, Jira, or Confluence efficiently, and resolve conflicts early are highly valued.
In essence, employers seek professionals who act as “bridges,” not “barriers.” The ability to communicate with clarity and lead through collaboration often determines who thrives in high-pressure DevOps environments.
5. Continuous Learning and Adaptability
The DevOps landscape changes faster than ever. New tools, frameworks, and methodologies appear every few months. Employers, therefore, prioritize engineers who embrace continuous learning.
Furthermore, adaptability is a key differentiator. Recruiters prefer those who quickly pick up new technologies and evolve with organizational needs. Certifications from AWS, Kubernetes, or Terraform show initiative, but practical application matters even more.
Additionally, curiosity drives innovation. Engineers who experiment with observability tools, serverless computing, or AI-driven monitoring stay ahead of the curve. Employers admire professionals who treat challenges as learning opportunities rather than setbacks.
At Techstack Digital, for instance, we’ve seen how teams that invest in upskilling deliver faster, more secure, and scalable solutions. In today’s market, adaptability isn’t optional — it’s survival. Continuous learners are the ones who keep DevOps pipelines modern, efficient, and future-ready.
Conclusion
The DevOps Engineer Job market continues to expand, but employers are getting selective. They now seek well-rounded professionals — those who blend technical expertise with communication, security, and adaptability. Furthermore, success depends on constant learning, automation excellence, and collaboration across teams. As businesses rely more on digital infrastructure, skilled DevOps engineers remain the backbone of reliable delivery. Whether you work in-house or with offshore software teams, staying proactive and curious will set you apart. The key takeaway: DevOps isn’t just a job title anymore — it’s a mindset that defines how the modern world builds and scales technology.